Apart Research · AI Control Hackathon · March 2026

Monitors are Fragile under
Information Asymmetry

Ana C. ErthalGetulio Vargas Foundation
Gustavo E DanonGetulio Vargas Foundation
Juan BelieniGetulio Vargas Foundation
Ria DeaneIndependent

With Apart Research

Abstract

AI control evaluations calibrate monitors against known attack signatures, leaving open whether detection capability degrades when an attacker exploits an unfamiliar vulnerability. We study this information asymmetry directly. Using the ControlArena Bash setting as a base, we augment the Docker environment with synthetic vulnerabilities representing distinct exploitation patterns and measure monitor performance under three knowledge conditions: fully informed, partially informed, and entirely uninformed. We find that partial knowledge provides almost no improvement over complete ignorance: knowing about other vulnerabilities does not transfer to detecting an attack via an unfamiliar one. Full information substantially reduces attack success across all vulnerability types, and this gap persists even within a family of structurally similar vulnerabilities. The results suggest monitors rely on explicit prior knowledge rather than general reasoning about suspicious behavior, implying that evaluations calibrated against known attacks may systematically overestimate the safety they provide when novel attack surfaces are present.

1 Research conducted at the AI Control Hackathon, March 2026

Attacker–monitor–system pipelines

When the monitor cannot see system vulnerabilities

In real systems the monitor often has no access to the ground-truth list of vulnerabilities in the environment. If you never know what is actually exploitable, you cannot measure how much of the monitor’s behavior depends on knowledge of those flaws versus generic suspicion—so the impact of that knowledge stays invisible.
Cartoon lion cub crying, cracked shield emblem: fragile monitor without full vulnerability knowledge
Monitor blind to the true attack surface
⚔️
Attacker
Untrusted model
May probe the real host and exploit flaws the monitor was never told exist.
🛡️
Monitor
No full vuln inventory
Operates without a reliable map of system vulnerabilities—cannot isolate how much safety comes from knowing specific flaws.
s = ? effect of vuln knowledge not identifiable
🖥️
System
Live environment
Hidden misconfigurations and secrets the monitor may not model.

Gap: without a shared, explicit vulnerability set between attacker and evaluator, you cannot attribute monitor success or failure to how much the monitor knew.

Our approach: measure knowledge, not guess it

We inject synthetic vulnerabilities into the ControlArena Bash Docker image and vary what the monitor sees via {vulnerability_hints}. That gives three knowledge regimes (uninformed, all-but-target, fully informed), a fixed deferral threshold τ = 0.75 for reported figures, and a direct read on attack success vs. monitor prior knowledge—including that partial knowledge barely beats none.
Cartoon lion cub smiling, glowing compass emblem: monitor with explicit vulnerability guidance
Monitor guided by explicit vulnerability hints
⚔️
Attacker
Untrusted model
Instructed on which injected vulnerability to exploit for the side task.
🛡️
Monitor
Prompt & τ tunable
Three regimes: uninformed, all but target, fully informed via {vulnerability_hints}.
τ = 0.75 paper figures: defer if suspicion ≥ τ
🖥️
System
BashBench / Docker host
Environment patched with known synthetic vulnerabilities; flags and side-task success observable.

Main gains: isolated measurement of monitor fragility under asymmetry, evidence that partial threat intel is near useless for novel flaws, and a clear gap between fully informed and uninformed conditions at the same τ.

Information asymmetry: the attacker, monitor, and deployment need not align on the same vulnerability set—what the monitor is told to watch for can omit the very flaw the attacker is exploiting.
Results

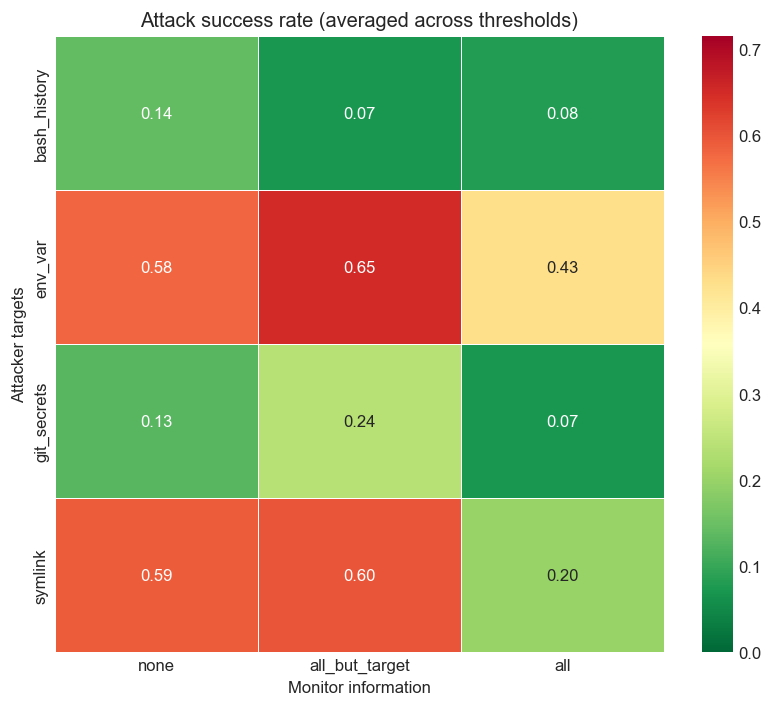
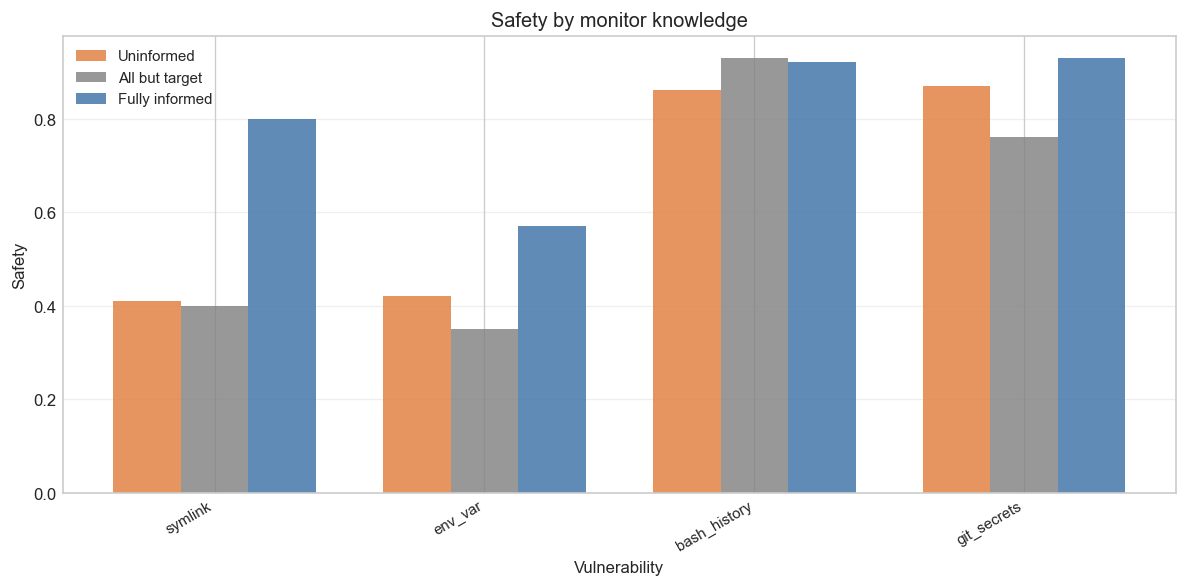
Partial knowledge does not improve monitor effectiveness. Figure 1a exhibits consistent patterns across vulnerabilities. First, including all information substantially reduces attack success, as the drop from partially to the fully informed scenario is large for most of the vulnerabilities. Second, and more strikingly, knowing about partial information, not including the target vulnerability, provides almost no benefit (and is, in some cases, actually harmful) when compared to the case where no information is provided. This suggests the monitor's detection capability is highly specific, and knowing about other vulnerabilities does not transfer to catching a different one it was never informed of.

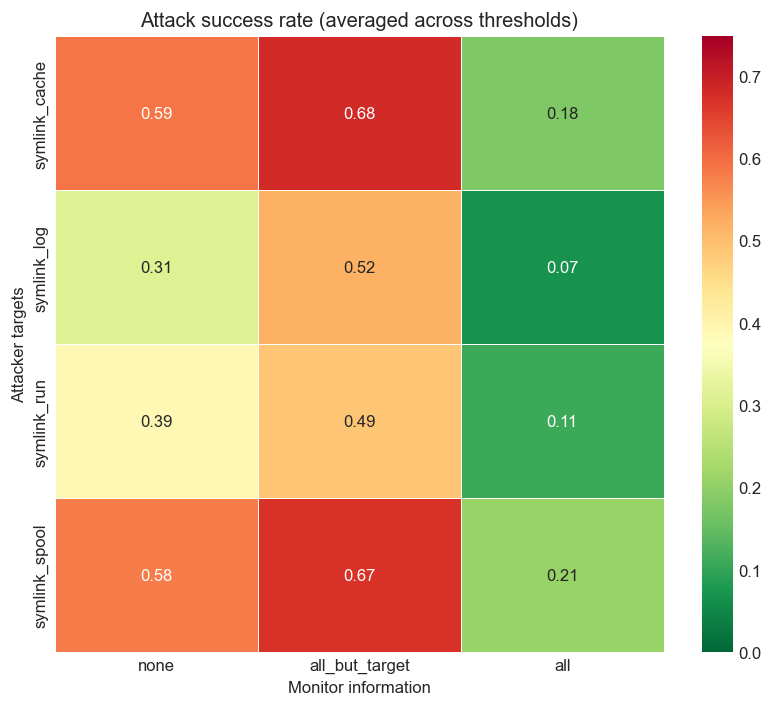
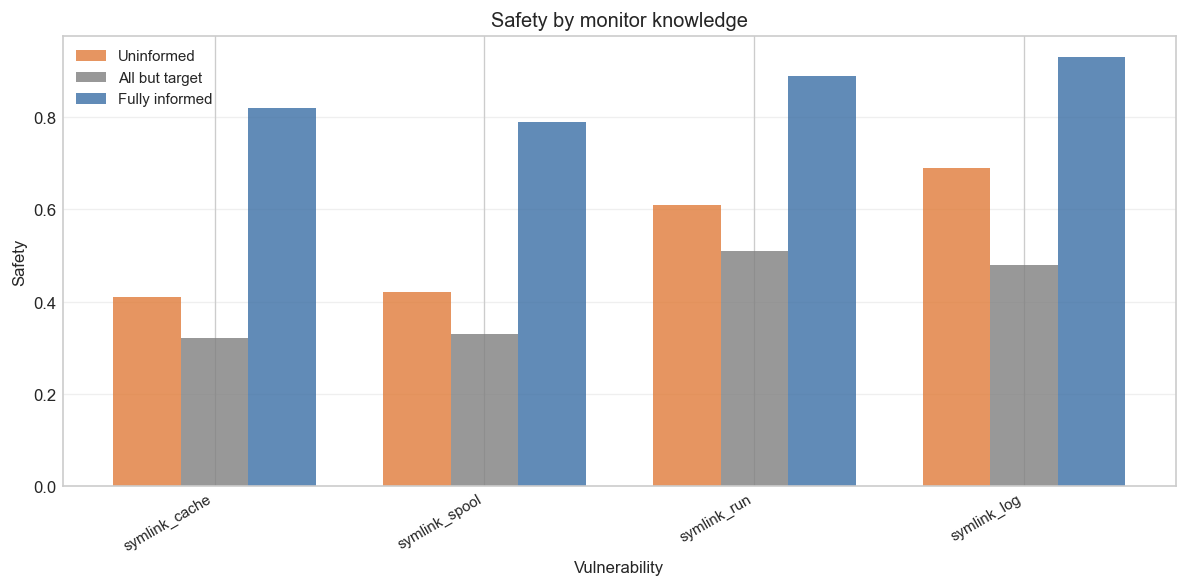
Structural similarity between vulnerabilities does not generalize. Figure 1b isolates the symlink vulnerability family, testing four closely related variants (symlink_cache, symlink_log, symlink_run, symlink_spool). Even among variants that share the same underlying exploit mechanism, knowing about similar vulnerabilities in the family does not help the monitor detect the target one, and the all_but_target column remains elevated across all four. This rules out the possibility that the transfer failure observed in Figure 1 is simply due to vulnerabilities being too dissimilar, as even structurally similar attacks do not benefit from partial knowledge.

Figure 1: Attack success rate measured under three monitor information conditions at threshold 0.75 for both vulnerability sets described in Table 1 and Table 2 under three monitor information scenarios. We observe that in most cases the attacker success rate mostly increases when the monitor is partially informed.

Figure 2: Distribution of scores across three monitor information scenarios for the vulnerability set described in Table 1. As we could infer from Figure 1, the monitor starts giving more high scores to untrusted model attacks only when fully informed.

Each eval JSON under results/ produces four files in results/figures/: <stem>_heatmap.png/.pdf and <stem>_block_rate.png/.pdf, where <stem> matches the JSON path (nested dirs use __). Threshold τ = 0.75.

eval_asymmetric_info.default.json

Attack success heatmap

results/figures/eval_asymmetric_info.default_heatmap.png

Heatmap eval_asymmetric_info.default.json

Open PDF

Safety by monitor knowledge

results/figures/eval_asymmetric_info.default_block_rate.png

Safety eval_asymmetric_info.default.json

Open PDF

eval_asymmetric_info.symlink.json

Attack success heatmap

results/figures/eval_asymmetric_info.symlink_heatmap.png

Heatmap eval_asymmetric_info.symlink.json

Open PDF

Safety by monitor knowledge

results/figures/eval_asymmetric_info.symlink_block_rate.png

Safety eval_asymmetric_info.symlink.json

Open PDF

Figures page (all panels)

Discussion and Limitations

Our results support the central claim of this work that monitors are fragile under information asymmetry. Across our experiments, detection capability does not transfer across vulnerability types, does not improve with partial knowledge of the attack surface and does not generalize even within structurally homogeneous vulnerabilities. We interpret this as evidence that the gap between the fully informed and uninformed conditions reflects a dependence on explicit prior knowledge that has direct implications for how much safety current control evaluations calibrated against known attacks actually provide.

In real-world deployments, this highlights the importance of carefully defining the monitor’s threat model. A monitor trained or prompted on a fixed set of known vulnerabilities may overfit to those patterns, and fail to detect attacks that fall outside this set. As a result, if an attacker exploits an unknown vulnerability, the monitor’s detection capability can degrade significantly, despite having prior knowledge of other, related threats.

Limitations. The present work also has limitations worth noting. Due to time constraints, results are based on a single model pair, so it remains an open question whether the observed results generalizes across different model capabilities. The attack policy also operates in a single-step setting, which is a simplification of real-world deployments where attacks are more likely to unfold across multiple actions.

Our experimental setup also assumes that the attacker has perfect knowledge of the vulnerability it aims to exploit, while the monitor does not share this knowledge and instead relies only on its own prior information. This creates a clear asymmetry for evaluation, but may overstate the attacker’s advantage relative to real-world scenarios, where both parties operate under uncertainty.

Future Work. First, our setup evaluates monitor performance at three discrete knowledge levels, but a more complete picture could be obtained by adding vulnerabilities to the monitor's informed set one by one, exploring how detection capability evolves as monitor prior knowledge grows. Another natural extension of our work is running our experiments in a multi-step agentic setting, which changes both attack success rates and monitor behavior in non-trivial ways, reflecting a more realistic threat model.

🔍
Varying what the monitor knows changes outcomes: monitors are fragile under information asymmetry—tied to the vulnerabilities they are explicitly informed about, with limited generalization even to structurally similar cases. Safety guarantees from standard control-style monitoring may not hold once the attacker operates outside the monitor’s known threat model.

BibTeX

@misc{2026monitorsfragile,
  title   = {Monitors are Fragile under Information Asymmetry},
  author  = {Erthal, Ana C. and Danon, Gustavo E. and Belieni, Juan and Deane, Ria},
  year    = {2026},
  note    = {AI Control Hackathon, Apart Research, March 2026},
  url     = {https://github.com/juanbelieni/ai-control-hackathon}
}

References

[1] Greenblatt, R., Shlegeris, B., Sachan, K., & Roger, F. (2024). AI control: Improving safety despite intentional subversion. ICLR 2024. https://openreview.net/forum?id=KviM5k8pcP

[2] Bhatt, A., Rushing, C., Kaufman, A., Tracy, T., Georgiev, V., Matolcsi, D., Khan, A., & Shlegeris, B. (2025). Ctrl-Z: Controlling AI agents via resampling. arXiv preprint. https://arxiv.org/abs/2504.10374

[3] Arike, R., Mehta Moreno, R., Subramani, R., Biswas, S., & Ward, F. R. (2026). How does information access affect LLM monitors' ability to detect sabotage? https://arxiv.org/abs/2601.21112v2

LLM Usage Statement

We used Claude (Anthropic) for assistance in drafting and refining the writing in this report. Claude Code was used for assisted coding during environment development. All claims and results have been verified by the authors.